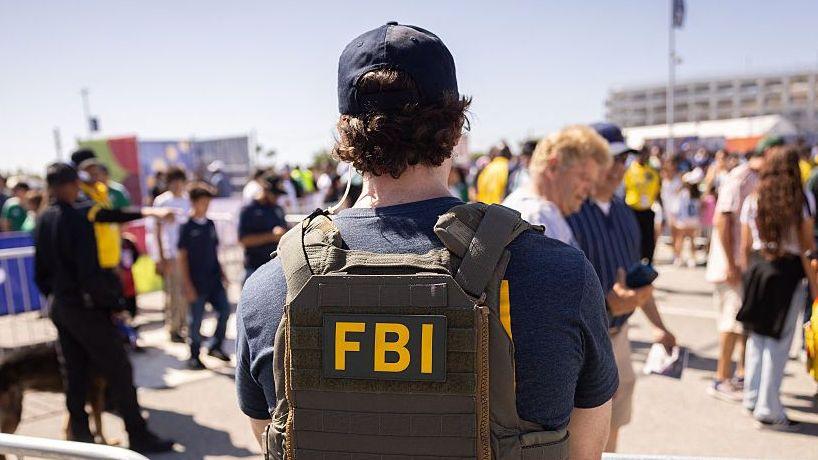
Police arrest a suspect linked to a hacking group that claimed a massive FBI data breach. The Dutch investigation identified a 24‑year‑old from Amsterdam as a key member of the ShinyHunters collective, which publicly announced in September that it had hacked the FBI’s Oracle‑cloud storage systems and released personal details for roughly 38,000 federal agents, including names, badge numbers, home addresses and phone numbers.
The suspect was apprehended on 15 September, prior to the actual breach, and police say he was also involved in attempts to incite foreign murders. His laptop contained extensive personal data and allegedly detailed plans for two murders to be carried out overseas, prompting a broader investigation into potential threats.
Dutch officials confirmed that they seized the suspect’s devices and discovered a large amount of sensitive information. “The ShinyHunters group is responsible for a large number of national and international victims,” said Stan Duijf, who leads the country’s cybercrime investigations. “It is good that we have been able to arrest a suspect in the investigation into this group,” he added.
The FBI’s director, Kash Patel, issued a statement thanking Dutch partners and announced that FBI teams were actively working with international law‑enforcement to identify further leads stemming from the arrest. Assistant director Brett Leatherman urged other potential members to surrender, warning that continued secrecy only deepens investigative reach.
ShinyHunters, believed to have origins in France, have previously targeted major companies such as Rockstar Games in April and the educational platform Canvas in May. The collective claimed to have exploited a vulnerability in the Oracle cloud system that the FBI uses for background checks and investigative files. In a dark‑web message they refused financial motives, demanding the FBI retract an advisory that had castigated them as “offended” by its portrayal of the group.
Officials note that the public service announcement on the FBI’s website continues to label ShinyHunters as “threat actors” who leverage false claims of access to coerce payments from victims and that the group’s scope extends across technology, finance, and retail sectors.