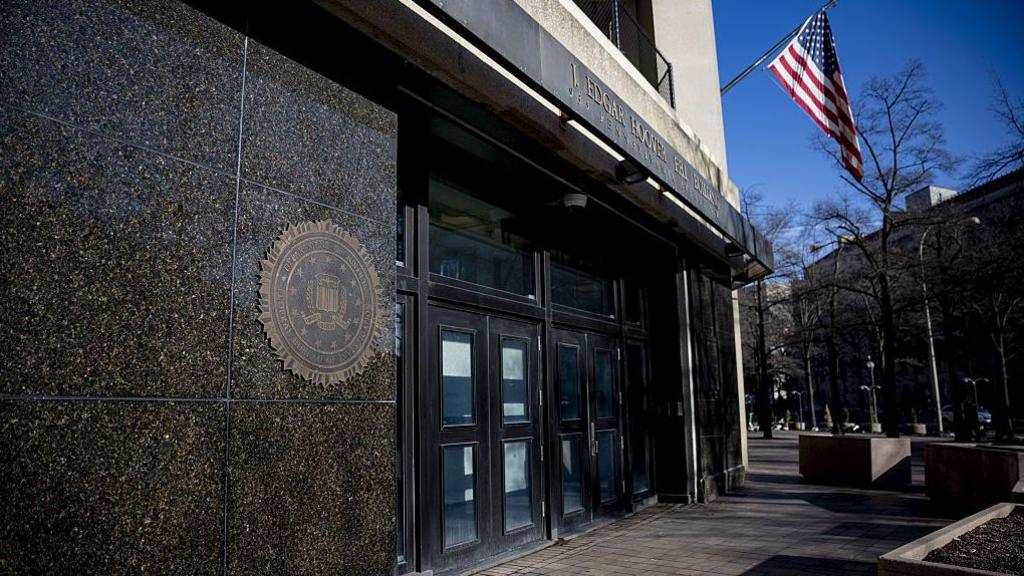
FBI data breach rattles agents; threat to expose private details
Thirty‑thousand FBI employees’ personal data has been stolen by the hacker collective ShinyHunters, according to a statement released to the BBC by current and former agents. The leak blankets home addresses, contact numbers, badge numbers and fitness‑for‑work medical reports, the investigators say.
Agents on Twitter and in private chats have voiced “shock,” fear for their safety and anger at the agency’s apparent negligence. “This is really bad for our undercover agents,” a former cyber‑investigator warned, describing the risk of phish attacks that could impersonate FBI officials.
ShinyHunters issued a four‑day ultimatum: they will publish the stolen data on the dark web unless the FBI retracts an advisory issued in May that the group claims “offended” them. The group is not demanding money; it demands political re‑traction. Their threat is a further blow to the FBI’s reputation, especially after a previous advanced attack that was considered “slick.”
Experts say the breach could also feed hostile foreign intelligence services seeking recruitment. The hackers’ hold on medical information—blood and urine test results, allergies, high cholesterol and other conditions—exposes even more risk, because that data can be targeted in tailored scams or political blackmail.
“The catalogue of data is huge and it will surface in the dark web for years,” said former Deputy Director of Cyber Cynthia Kaiser, who now heads the Halcyon research centre. In the meantime, agents have been advised to use services like DeleteMe to scrub data broker sites, though many say that is an inadequate response.
FBI Director Kash Patel faces a crisis of leadership amid this incident, as the agency struggles to explain how a supposedly top‑notch operation could be breached by a hacking group that is not even considered “high‑grade” by conventional standards.