In brief
An Airbus A321 operated by Wizz Air, flying from Milan to Warsaw, was forced to divert to Vienna on Nov. 5 after receiving a threatening e‑mail. The email, reported as vague and unspecific, prompted authorities to hold the aircraft for safety checks. While the incident was handled without incident, the precise content of the threat and its source remain unknown.
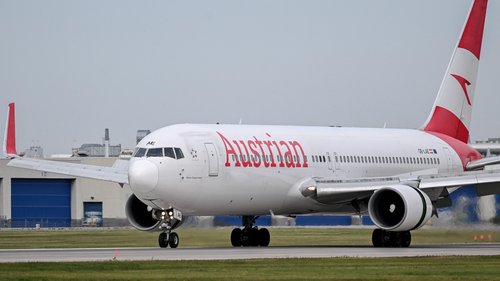
A Wizz Air Airbus A321, bound from Milan to Warsaw, made an unscheduled landing at Vienna International Airport on November 5, 2026, after the crew received an email containing a vague threat. The diversion, reported by Xinhua and corroborated by the Austrian daily Kronen Zeitung, prompted the airport to assess the aircraft for potential security risks.
The e‑mail that prompted the stop‑over was described by sources as “vague” and did not specify any weapon or intent. No details of the sender were released, and the airline has not publicly confirmed the threat’s content beyond the reported lack of concrete instructions. The flight crew followed standard protocol, contacting Vienna air traffic control and requesting an authorized landing while awaiting further instructions.
Upon arrival, airport security teams conducted a routine inspection of the aircraft as is normal in such cases. According to German‑language press reports, the crew encountered no hazardous materials or signs of sabotage. The aircraft landed without incident, and passengers were subsequently escorted to the terminal for a brief waiting period while security measures were finalized.
Vienna Airport also received a separate e‑mail concerning four flights, according to a brief announcement from an aviation security office. While the details of that message were not fully disclosed, the notification triggered a precautionary review of the other aircraft scheduled to land that day. No other flights were diverted or delayed as a result of the information, and the airport’s operations returned to normal after the initial assessment.
Wizz Air has not issued a statement regarding the incident, and its spokesperson has declined to comment on the security protocols for the flight. The airline’s parent company reported that the incident did not impact subsequent flights, though they emphasized that safety remained paramount. Austrian aviation authorities have stated that they will keep additional surveillance of the airport’s inbound traffic, especially over the next few days.
Authorities have not identified the sender of the email threat, nor have they confirmed whether the threat represented a credible risk. The investigation into the origin of the message is ongoing, according to a preliminary police brief. Aviation security experts note that the use of e‑mail as a threat vector has increased in Europe, prompting broader discussion about cybersecurity in passenger transport.
While the presence of a threat email forced a temporary diversion, no injuries or equipment damage were reported. Passengers reportedly wait for additional information before being re‑boarded to Warsaw, and the flight departed safely after an approximately eight‑hour delay. The incident demonstrates the protocols used by airlines and airports when confronted with adverse digital communications.
---
Uncertainties remain regarding the exact content of the e‑mail, its sender, and the potential motives behind the threat. The investigation by authorities has yet to disclose whether the threat was credible or intended to influence flight routes, and further details may emerge in the coming days as security agencies pursue additional leads.